Risk Management and Risk Governance
Risk Management
ORIX has established a company-wide risk management system to accurately identify and appropriately manage the various risks associated with our business activities. The Board of Directors has ultimate oversight responsibility for the overall management of the company, including risk management, and determines company-wide policies and basic frameworks.
The Representative Executive Officer is responsible for establishing and maintaining the risk management systems necessary for the operation of each business division based on the company-wide risk appetite which is in turn based on the business strategy established by the Board of Directors. Responses to various risks are decided through deliberation bodies such as the Executive Committee, which is chaired by the CEO, and the Investment and Credit Committee. The status of risk management in the business divisions is monitored through coordinated efforts of the internal control-related functions. Specifically, each business division formulates within its annual business plan a risk management plan which takes into account the risks specific to its business. Furthermore, through an annual self-verification program, the division identifies risks that could have a significant impact on business operations and verifies whether the division is adequately addressing these significant risks. The ERM department continuously evaluates company-wide risks, including credit risk, market risk, liquidity risk, and operational risk, and provides support for improvements as necessary. Through these procedures, we secure the effectiveness of company-wide risk management.
Risk Governance
ORIX has established and operates an internal control system that takes into account risk management, compliance, Group company management, audit systems, and other aspects in order to respond quickly and flexibly to changes in the business environment and enable efficient business execution and effective management. The Board of Directors bears ultimate responsibility for this risk governance system and its operation, and determines the overall approach. ORIX has established the following division of roles based on the three-line defense model in order to implement robust risk governance. Business divisions (first line) identify, assess, and manage risks related to their assigned business operations in accordance with the policies and frameworks established by internal control-related departments. Internal control-related departments (second line) monitor the risk response status of business divisions from a specialized, cross-company perspective and encourage improvements as necessary. The internal audit department (third line), independent from business divisions and internal control-related departments, verifies and evaluates the effectiveness of the entire risk governance process and recommends corrective measures if any deficiencies are identified. In addition, external and internal reporting hotlines complement our risk governance as a mechanism for identifying signs of risk incidents.
Summary of ORIX's Internal Control System (with some additions) (As of June 30, 2026)
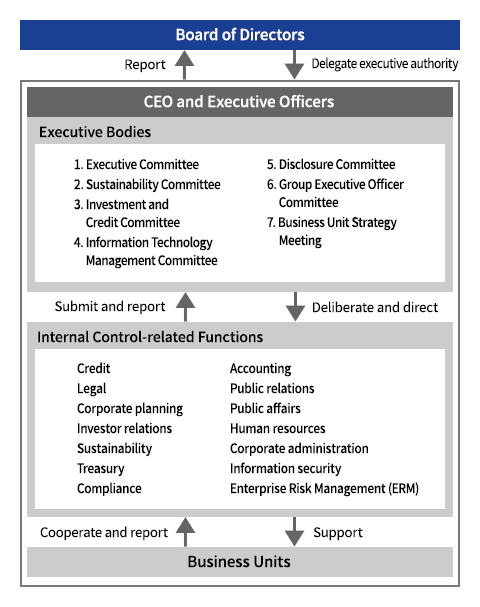
Executive bodies manage risk under the supervision of the Board of Directors. These bodies and their responsibilities are as follows.
| Executive Bodies | Roles |
|---|---|
| Executive Committee | Deliberates on capital policy, asset and liability management, accounting and taxation, compliance, personnel, and other important management matters. Reports to the Board of Directors as necessary. |
| Investment and Credit Committee | Deliberates on specific investment and lending transactions. If needed, matters are additionally deliberated by the Executive Committee and reported to the Board of Directors. |
| Information Technology Management Committee | Deliberates on important matters concerning fundamental IT policies and strategies as well as the introduction and maintenance of IT systems. |
| Sustainability Committee | Deliberates on important matters related to sustainability. Reports to the Board of Directors as necessary. |
| Disclosure Committee | Aggregates important information, considers needs and methods for timely disclosure, and coordinates disclosure. |
| Business Unit Strategy Meeting | A forum for business unit managers to discuss strategy and changes in the business environment with top management. |
| Group Executive Officer Committee | A forum for all executive officers to share important information related to Group business administration. |
RCSA Centered Annual Cycle
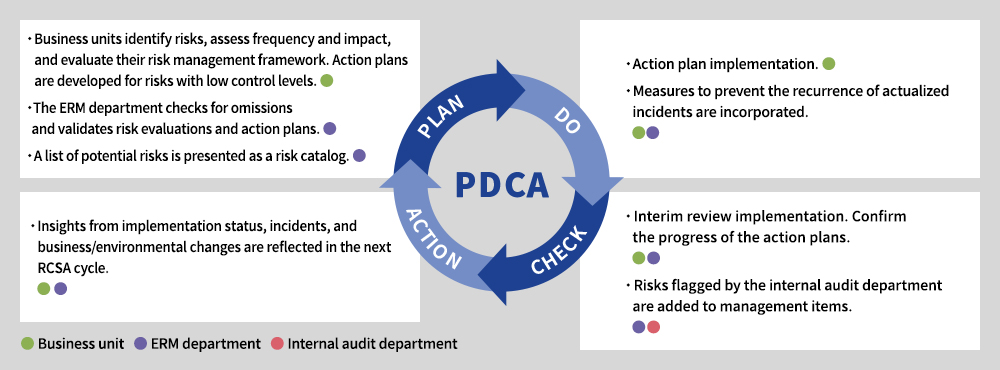
As part of its preventive efforts, the Company conducts a Risk Control Self-Assessment (RCSA) annually with the objective of establishing an appropriate risk management framework. In addition to identifying and assessing risks and formulating action plans at the beginning of each fiscal year, risks are reviewed through a cycle that includes a mid-year review, during which additional risks may be identified and existing action plans revised as necessary.
Through the RCSA process, the Company confirms that operations are conducted in accordance with applicable rules and regulations while each department identifies and assesses the operational risks inherent in its activities and develops and implements action plans to mitigate those risks. The ERM department, which oversees the RCSA process, creates and shares a “risk catalog” that lists risk items based on specialized perspectives from corporate functions such as Legal, Compliance, and Information Security, as well as information on external incidents. This promotes comprehensive risk identification by each department. In addition, the ERM department reviews the appropriateness of the action plans and risk assessments formulated by each department and continuously verifies whether risk management practices are being carried out in line with actual business operations. Risk assessments and action plans are also subject to approval by the top management of each department.
During the year, progress is monitored through mid-year reviews, during which both the respective departments and the ERM department confirm whether action plans are being implemented as scheduled. The review process also incorporates measures to prevent the recurrence of actualized incidents and, where appropriate, findings from the Internal Audit function, ensuring the continuous identification, monitoring, and management of risks. Going forward, while each department will continue to enhance its own risk management framework, the ERM department will identify risks associated with priority businesses and other risks requiring focused management, provide hands-on support where necessary, and verify the effectiveness of these efforts on an ongoing basis.