Information Security
Information Security at ORIX and Information Security Governance Structure
ORIX recognizes that risks related to Information /Cyber security are an important management issue, and strives to ensure appropriate protection of information and safe management of information assets. These ideas and policies on information security are stipulated in the Information Security Policy. We established information security management rules as internal regulations, which stipulate appropriate use of information and information systems by officers and employees, as well as information security management systems, basic policies, management standards and cyber security incident response.
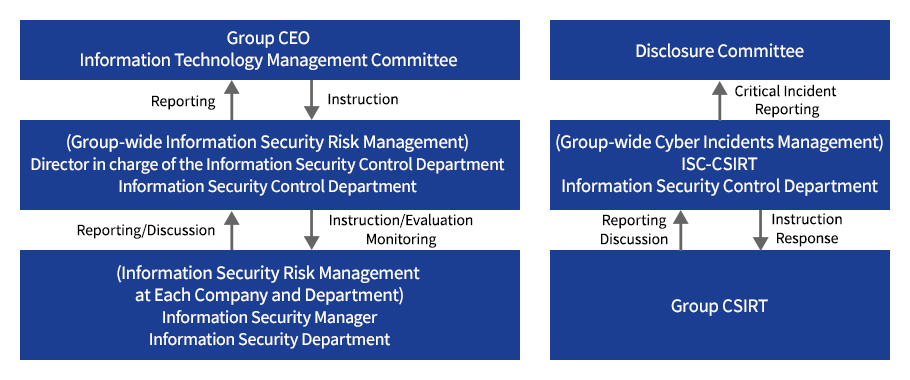
Information Security Governance Structure
Information Security Management Measures
In order to manage information security risks, ORIX Group has established the Information Security Management Rules and Minimum Security Standards, taking into account international frameworks such as ISO 27001 and NIST.
The Information Security Management Rules set forth requirements relating to information management, security in outsourcing, personnel security, physical security, technical security, and information security incidents. Each company and division within ORIX Group implements control measures based on its own risks, taking into account the nature of its business, the information it possesses, anticipated threats, and regulatory requirements.
In addition, the Minimum Security Standards prescribe the minimum control measures that all ORIX Group companies, both in Japan and overseas, must comply with regardless of company size.
Response to Information Security Incidents
ORIX Group has established ORIX-SIRT as an organization that supports cyber incident response across the Group. The CSIRT of each ORIX Group company and division, with the support of ORIX-SIRT, maintains reporting frameworks and response procedures for information security incidents. In addition, ORIX Group conducts exercises that assume the occurrence of major cyber incidents, and verifies inter-organizational coordination, response procedures, and management decision-making processes from a business continuity perspective while continuously implementing improvements.
If officers or employees identify an information security incident, vulnerability, or suspicious activity, they report it through the designated reporting channels established by their respective company. The division where the incident occurred works closely with its CSIRT and relevant divisions to respond promptly. Reports are also made to affected stakeholders as necessary. In the event of a significant cyber incident, a framework is in place to report the matter to the CEO and the Disclosure Committee and to carry out timely disclosure and other required actions in accordance with internal regulations.
Third-Party Risk Management
ORIX Group conducts assessments of outsourcing providers and cloud services to address information security risks arising from third parties, including outsourced services and the use of cloud services. These assessments cover areas such as information security management, access management, vulnerability management, incident response, disaster recovery, and backup measures.
Threat Monitoring
ORIX Group continuously monitors information security threats affecting critical systems and IT infrastructure through the use of SIEM and log monitoring services. Detected incidents and indicators of compromise are addressed promptly in accordance with the incident response procedures described above.
Cyber Security Training
Cyber security training and phishing email training are available to all Group officers and employees throughout the year. In the fiscal year ended March 31, 2026, 38,431 people received training.